

Enterprise-grade security. Any size company.
Ten-person startup or public company — you get our full bench of expertise. We don't cut corners because you're small.
01
─ Our Services
What we do
It's not complicated, but every aspect is done in depth.
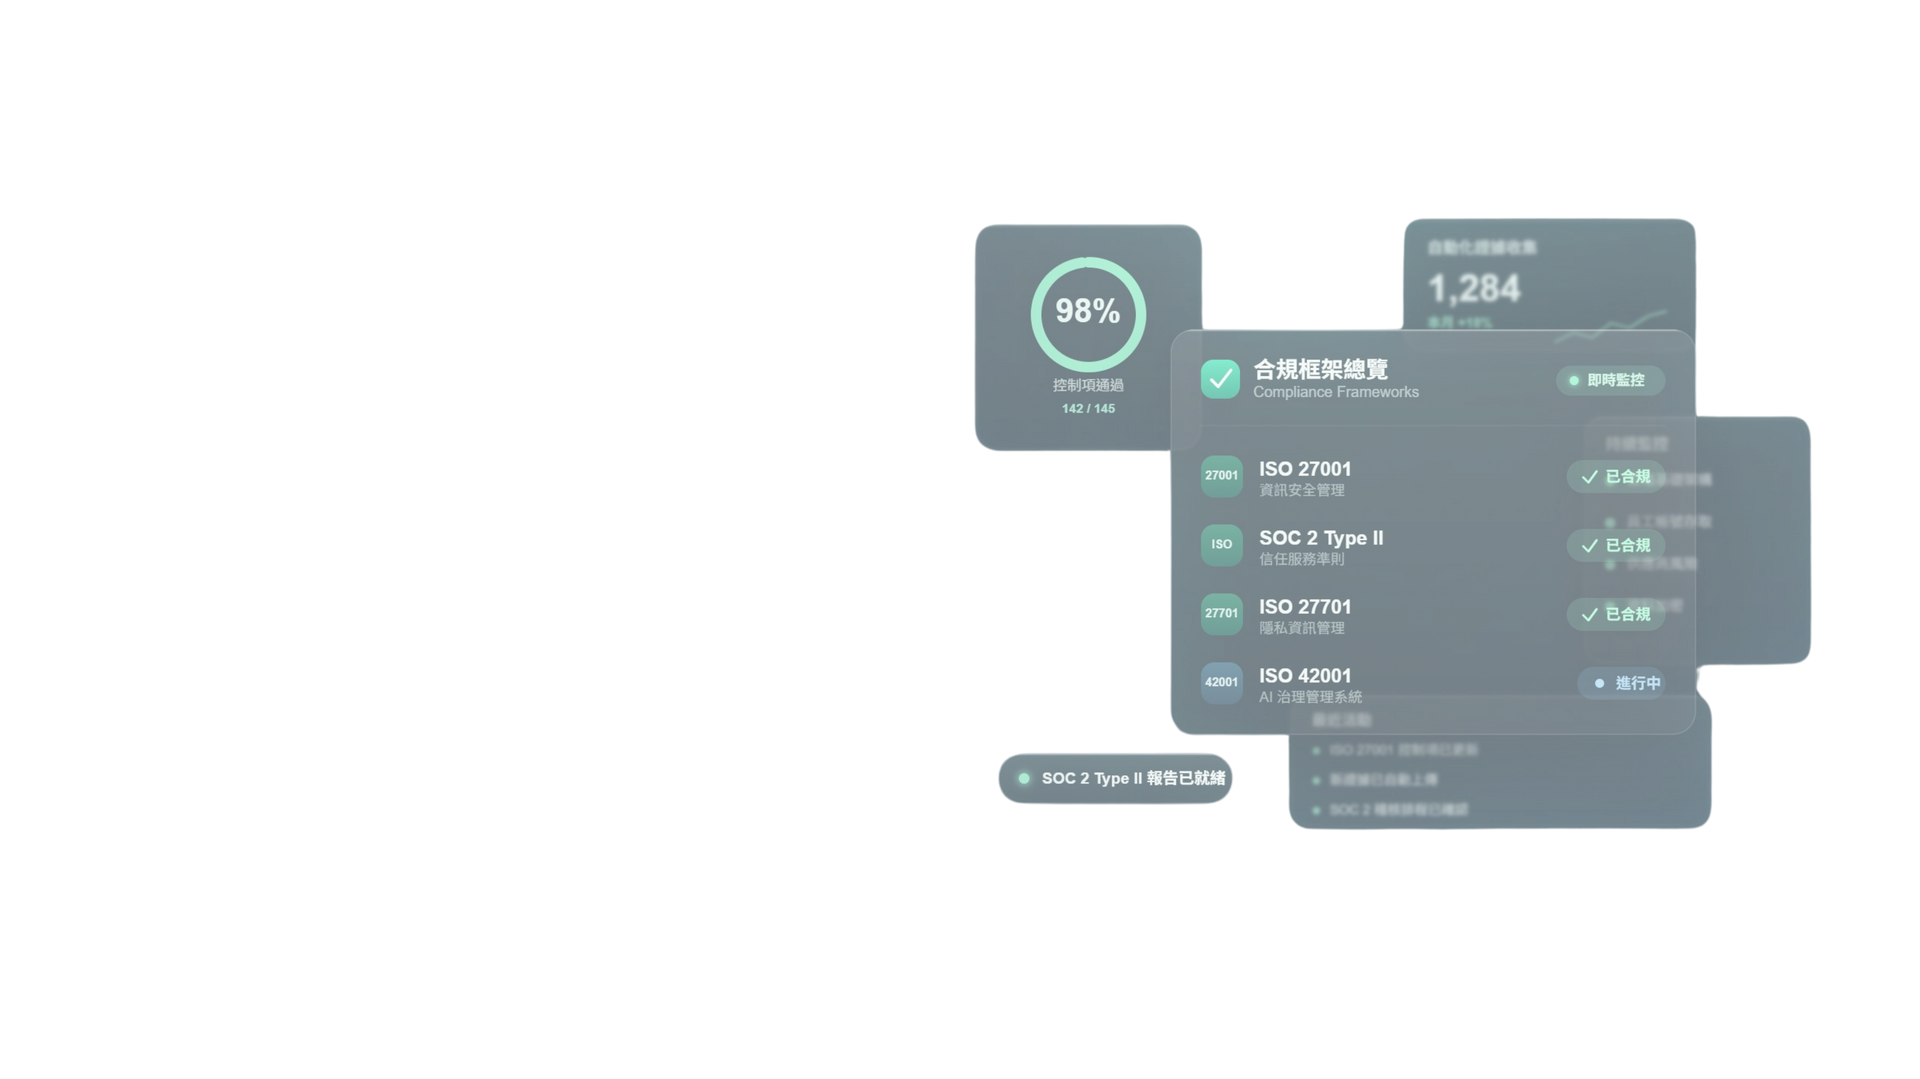
International cybersecurity and privacy standards
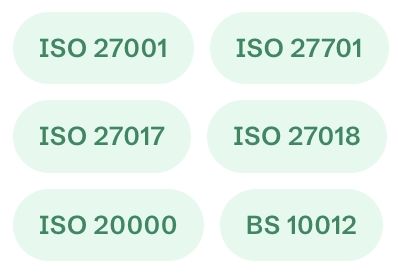
Establish an information security and personal data management system that can be trusted by international clients and regulators, covering everything from documents and processes to audits in one go.
AI governance framework
To establish the first governance foundation for new risks in the AI era, and to help companies establish an accountable and controllable governance framework while introducing AI.
Industry-specific compliance
TISAX (Automotive Supply Chain) | SOC 2 Type 1 & 2 (SaaS for the US) | EU CRA (Products Sold to the European Union) are key entry tickets to the international supply chain and overseas markets.
Cybersecurity technical services
From source code scanning, vulnerability scanning, and penetration testing to social engineering drills and training—we go beyond just submitting reports; we assist in patching and improving systems.
International Security & Privacy Standards
An ISMS and privacy program your customers, auditors, and regulators will actually trust. We handle the policies, the controls, and the audit — end to end.
AI Governance
AI expands your risk surface. We help you stand up real AI governance — clear ownership, accountability, and guardrails — before you scale.
Industry-Specific Compliance
TISAX for automotive supply chains. SOC 2 Type I & II for SaaS selling into the US. EU CRA for products shipping into Europe. The credentials that clear procurement and get the deal signed.
Technical Security Services
Source code review, vulnerability scanning, penetration testing, social engineering assessments, and security awareness training. We don't just hand you a pen test report — we help you remediate every finding.
02
─ Our Partners
Our working partners
Collaborate with professional teams in various fields to help enterprises achieve more comprehensive cybersecurity and compliance.
02
─ Our Partners
Who we work with
We team up with specialists in adjacent disciplines, so your security and compliance coverage has zero blind spots.
03
─ Client Voices
Companies like yours have already chosen FEACE
From listed companies to startups, from manufacturing to AI.

Initially, we were just looking for a certificate to get by. Unexpectedly, when Fiss first came, they didn't rush to sell us a solution, but instead spent most of the day figuring out what our company did. Later, when they wrote the program, my colleague said, "I can understand this and I can do it," something that had almost never happened before. The consultant accompanied us throughout the audit day; that sense of security, that feeling of having someone back you up, is something that price can't buy.
— Chief Information Officer of Listed Electronics Manufacturers
We consulted several consultants about ISO 42001, but most of them just kept applying the same old ISO 27001 framework. FAI was different; they genuinely understood AI—they could discuss with our engineers everything from training data risks and how to backtrack on model errors to the supply chain terms of third-party APIs. In the end, we not only got the certification, but our team also truly understood how to use AI responsibly. For a company that considers AI a core competency, this certification is the foundation of trust for negotiating partnerships with clients.
— AI model service provider Censor
We've had bad experiences with consultants before—they make all sorts of promises before signing the contract, but then disappear once we get the certification. Fischer is different; they value relationships more than the case itself. They proactively remind us of any changes in regulations or new requirements, so we don't have to keep asking. The most reassuring thing is knowing that when we encounter problems, there's a team that truly understands our company and cares about us.
— Chief Reporter of Listed E-commerce Platforms
We're a traditional manufacturing company, and we're usually most afraid of consultants using jargon we can't understand. What's remarkable about Fischer is that they speak in plain language, translating cybersecurity requirements into things we could actually do on-site. The implementation process wasn't chaotic; everything that needed to be done was clearly explained beforehand. We passed the ISO test smoothly on our first try, and the team wasn't overwhelmed, for which I'm very grateful.
— General Manager of a metal processing industry with 100 employees
03
─ Client Voices
Companies like yours already work with FeAce
Public companies and startups. Manufacturers and AI labs.
"Honestly, we went in with a 'get the certificate and move on' attitude. FeAce's first visit wasn't a pitch — they spent most of the day understanding what our company actually does. When the procedures came out, my team said 'I can read this, and I can do this,' which had almost never happened before. On audit day the consultant was with us the whole time. That kind of reassurance is worth more than the fee."
— IT Director, publicly traded electronics manufacturer
"We talked to several consultants about ISO 42001, and most of them were just recycling the 27001 playbook. FeAce was different — they actually understand AI. They could sit with our engineers and talk about training-data risk, how to trace a model failure, third-party API supply-chain terms. We didn't just get the certificate; the team now knows how to use AI responsibly. For a company built on AI, that certificate is the basis of trust with every customer."
— CISO, AI model service provider
"We'd been burned by consultants before — big promises up front, then gone the moment the certificate arrived. FeAce treats the relationship as more important than the project. When regulations change or new requirements come up, they flag it before we ask. Most of all, when we hit a problem, there's a team that really understands our business and takes us seriously."
— CIO, publicly traded e-commerce platform
"We're a traditional manufacturer, and our biggest fear was a consultant full of jargon we couldn't follow. FeAce speaks plainly — they turned the security requirements into things our shop floor could actually do. The rollout didn't turn the company upside down; whatever we needed to prepare was explained up front. We passed our first ISO audit without the team being run ragged. I'm grateful for that."
— General Manager, 100-person metal-processing company
By the Numbers
FEACE's Achievements
We've done everything from startups to publicly listed companies.
Since its inception, FEACE has mentored a wide range of clients, including listed companies, startups, and SMEs, spanning multiple industries—these figures represent our most authentic resume.
35
Serving enterprise clients
10
Listed and OTC corporate clients
12
Lead Auditor Certification
6 M
Average certification period
Our clients range from startups with ten employees to listed groups with over ten thousand employees.
Spanning industries including electronics manufacturing, semiconductors, fintech, AI, logistics, and cultural performances.
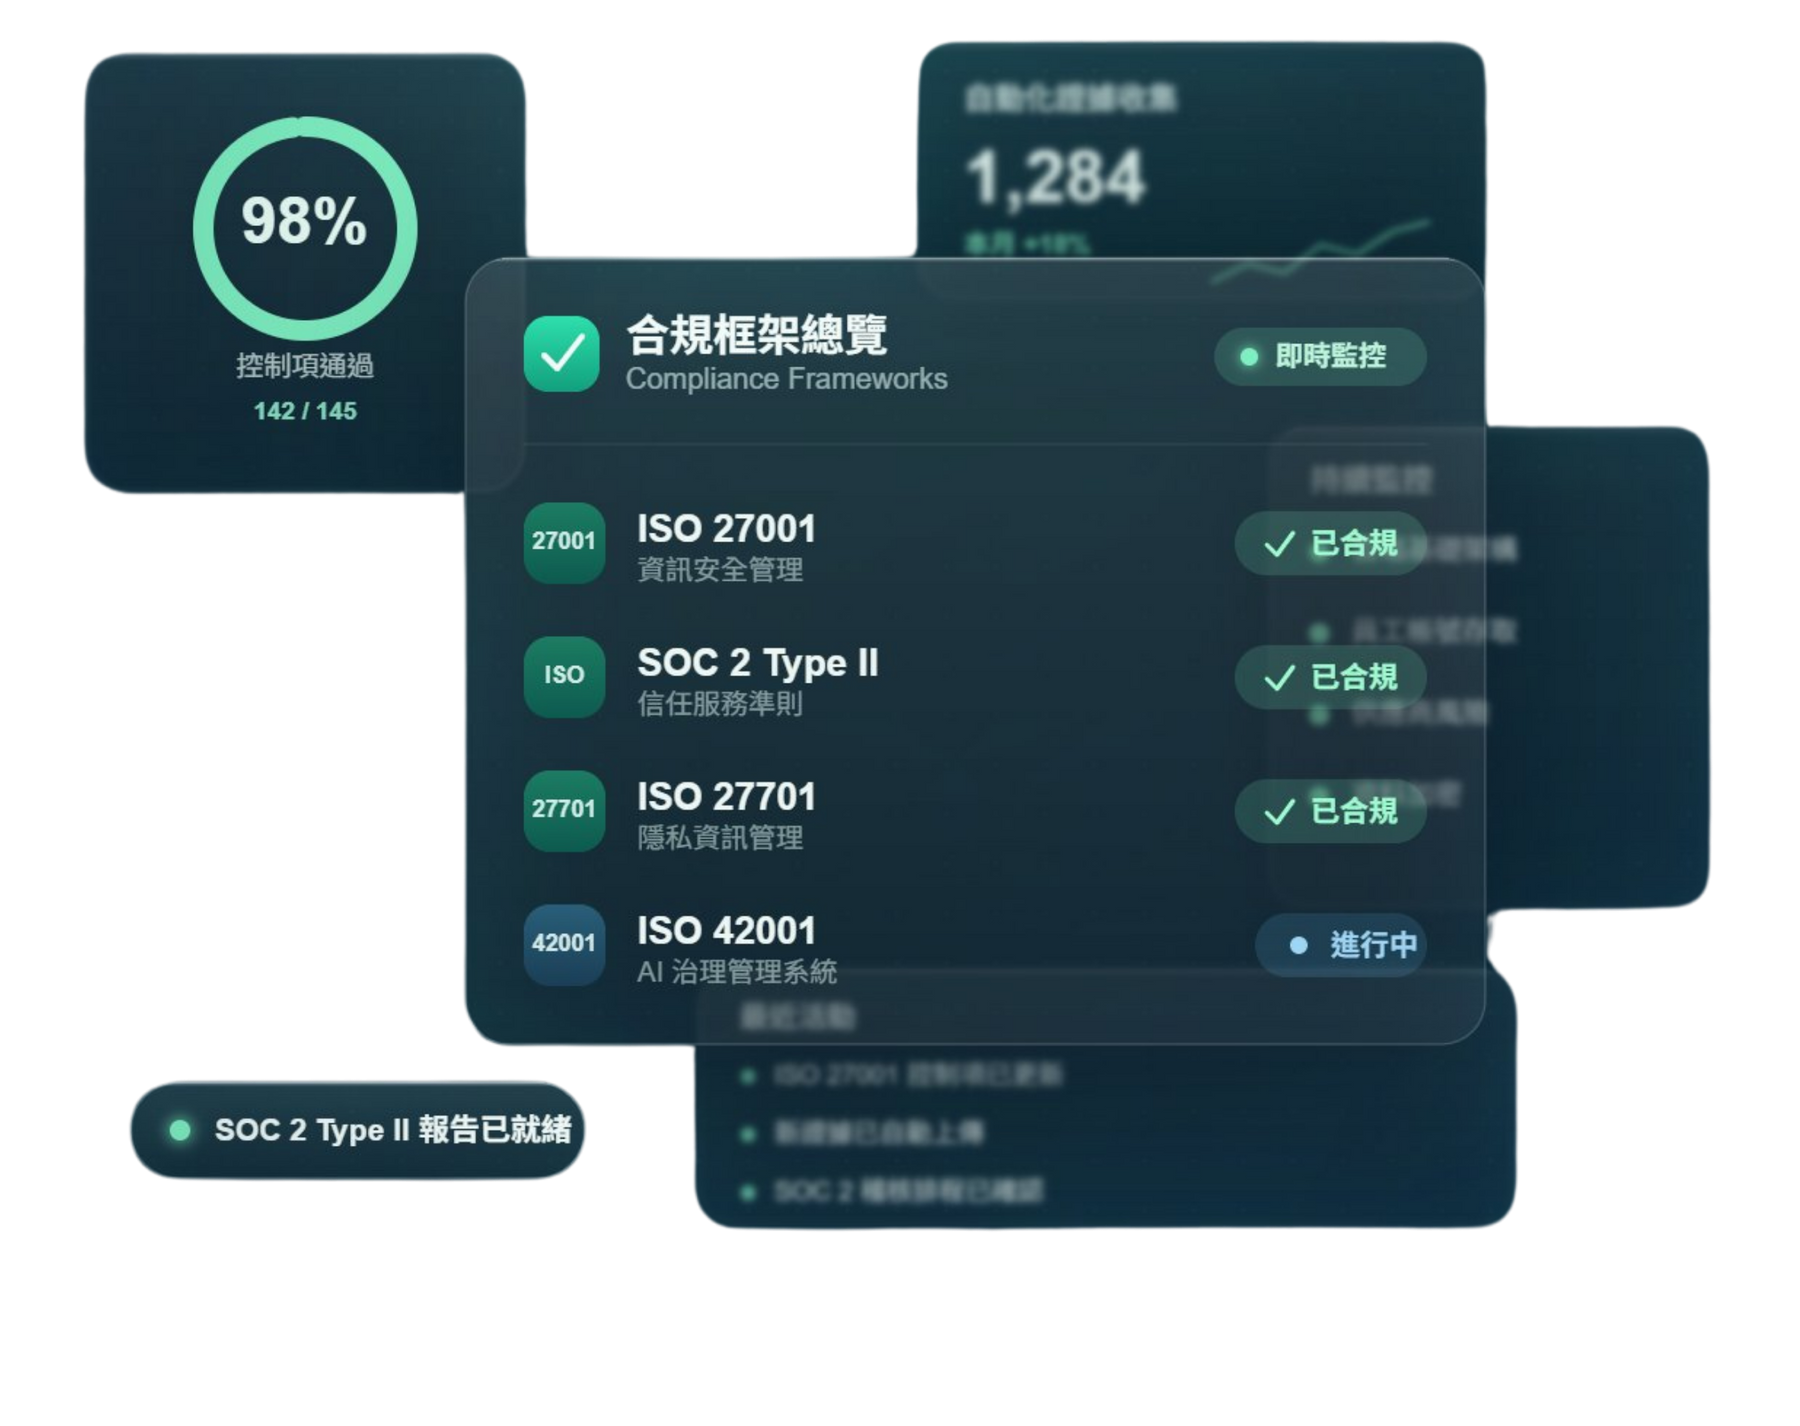
Service standards ISO 27001/27701/27017/27018/42001, TISAX, SOC 2, EU CRA, Cybersecurity Law
* The average certification period varies depending on the scope of the project and your company's internal coordination. The actual certification results are subject to the evaluation of a third-party verification agency.
By the Numbers
The FeAce Track Record
Startups to public companies. We've done both.
Since day one, FeAce has advised public companies, startups, and SMBs across a wide range of industries. These numbers back it up.
80+
Enterprise clients
10+
Public-company clients
12+
Lead Auditor credentials
6 months
Average time to certification
Clients: from ten-person startups to publicly traded groups with 10,000+ employees
Industries: electronics manufacturing, semiconductors, fintech, AI, logistics, cultural & creative, and more
Standards: ISO 27001 / 27701 / 27017 / 27018 / 42001 · TISAX · SOC 2 · EU CRA · Taiwan Cyber Security Management Act
* Average time to certification varies with project scope and the client's internal availability. Certification decisions rest with the third-party certification body.
04
News & Insights
Latest News and Columns
Stay informed about international standards developments and compliance practices.
2026.06.02
Regulatory Updates
2026.05.26
Standard Analysis
2026.05.20
Industry Trends
04
News & Insights
Latest News and Columns
Stay informed about international standards developments and compliance practices.
2026.06.02
Regulatory Updates
2026.05.26
Standard Analysis
2026.05.20
Industry Trends

- Contact Us
Let's map out where you need to be

service@feaceint.com

Office
5F, No. 390, Sec. 1, Wenhua 2nd Rd., Linkou Dist., New Taipei City, Taiwan (R.O.C.)
Contact Us
We'll get back to you within one business day.